Enterprise software is no longer just an IT concern, it is a regulatory, financial, and reputational risk surface. According to the Standish Group CHAOS Report, only around 31% of software projects succeed outright; roughly 50% are “challenged” completed over budget, over schedule, or with reduced scope and the remainder are canceled before completion.
Despite Agile and DevOps adoption, many enterprises lack a formal SDLC governance model, resulting in:
- Uncontrolled scope expansion
- Security and compliance gaps
- Poor audit traceability
- High operational risk
In more than a decade of working with enterprise transformation programs, one pattern is consistent: organizations with a structured phase gate process and clearly defined software lifecycle governance controls deliver more predictable outcomes and experience fewer audit escalations.
This article explains how to design, implement, and scale a modern SDLC governance model aligned with enterprise SDLC framework principles.
Key Takeaways
-
- 1An SDLC governance model is a structured framework of policies, approval gates, risk controls, and accountability that guides software from idea to retirement
- 2A phase gate process divides development into stages separated by formal review checkpoints, so work only advances when defined criteria are met
- 3Governance and agility can coexist — modern enterprises embed governance directly into CI/CD pipelines rather than treating it as a separate bureaucratic layer
- 4ISO/IEC 12207, COBIT, NIST RMF, and ISO 31000 are the primary standards enterprises use to structure governance and risk controls
What Is an SDLC Governance Model?
An SDLC governance model defines how software initiatives are controlled, reviewed, approved, and monitored across their lifecycle.
It ensures:
- Strategic alignment
- Risk visibility
- Compliance enforcement
- Budget discipline
- Documentation traceability
Unlike lightweight project tracking systems, an SDLC governance model formalizes accountability across executive sponsors, architecture boards, security teams, and delivery squads.
This is sometimes referred to simply as software governance or a software development governance model the terms are used interchangeably across enterprise and vendor documentation.
Core Objectives of Software Lifecycle Governance
Software lifecycle governance aims to:
- Standardize decision-making
- Reduce project variance
- Embed risk management in software development
- Ensure regulatory readiness
- Improve delivery predictability
According to ISO/IEC 12207 and COBIT frameworks, governance must include policy enforcement, oversight structures, and measurable controls.
Understanding the Phase Gate Process in Enterprise Environments
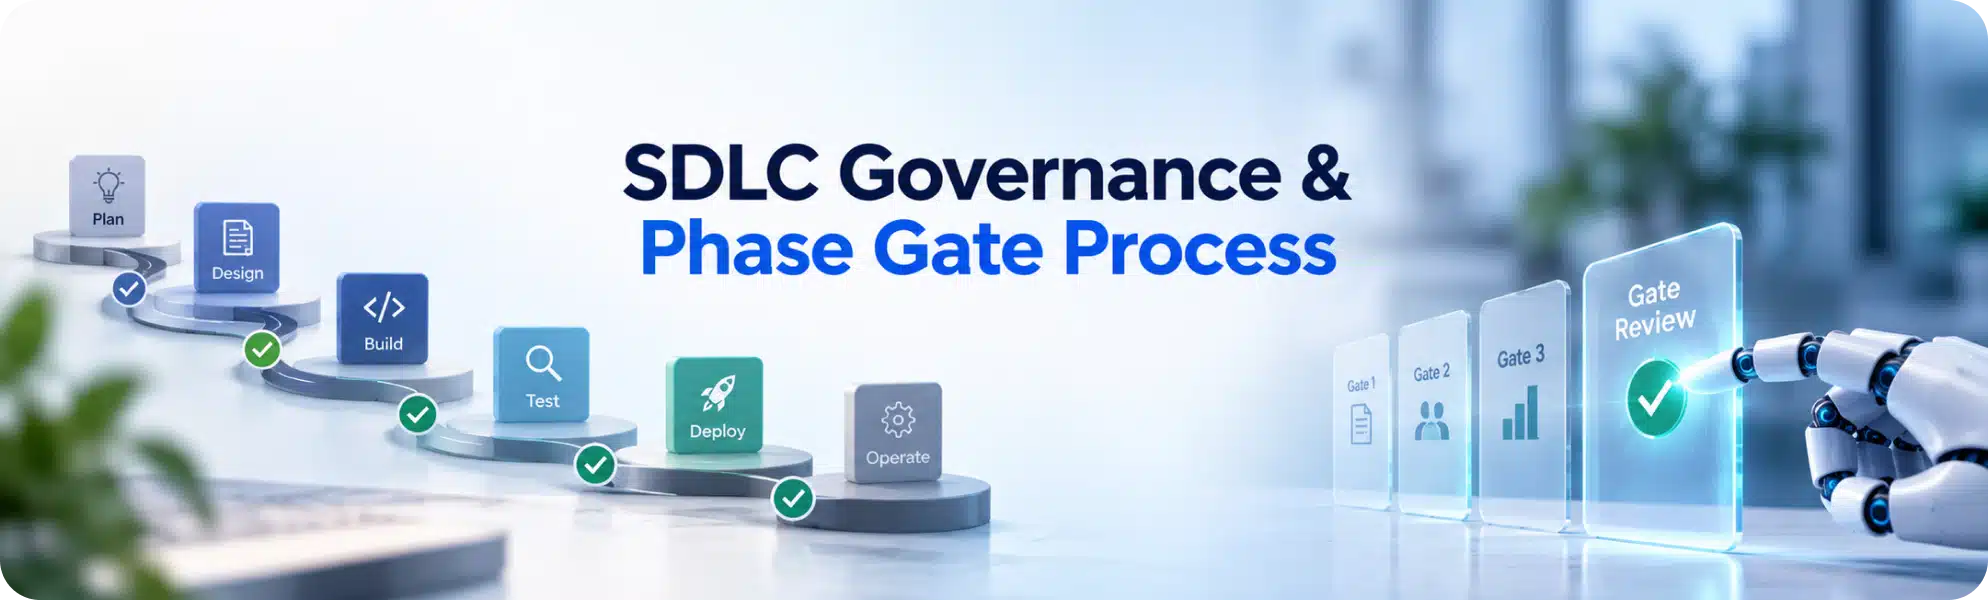
A structured phase gate process is the operational engine of a strong SDLC governance model.
What Is a Phase Gate Process?
A phase gate process divides development into stages separated by formal review checkpoints (“gates”). Each gate evaluates:
- Deliverable completeness
- Risk exposure
- Budget compliance
- Regulatory adherence
Only when gate criteria are met can the initiative move forward.
Typical Enterprise Phase Gates
| Typical Enterprise Phase Gates | |
|---|---|
|
Concept Gate |
Business value validation |
|
Requirements Gate |
Scope and compliance review |
|
Architecture Gate |
Design and integration review |
|
Security Gate |
Risk and control validation |
|
Pre-Production Gate |
Operational readiness |
|
Post-Implementation Gate |
Performance review |
When properly implemented, a phase gate process improves transparency and reduces rework costs.
Designing an Enterprise SDLC Framework with Governance Controls
An enterprise SDLC framework integrates governance without stifling innovation.
Governance Components in a Modern SDLC Governance Model
A mature SDLC governance model includes:
- Clearly defined RACI matrices
- Standard documentation templates
- Digital approval workflows
- Risk scoring dashboards
- Compliance tracking systems
These components support structured software lifecycle governance while allowing agile teams to move efficiently.
Governance in Agile and DevOps
Contrary to common belief, governance and agility can coexist.
- Use automated digital gates
- Integrate approvals into CI/CD pipelines
- Capture audit evidence automatically
- Embed risk management in software development dashboards
This evolution ensures governance supports, rather than blocks, innovation.
Risk Management in Software Development
Risk management in software development is foundational to effective governance. Without risk controls, projects expose enterprises to financial, operational, and regulatory consequences.
Types of Risks Managed Under an SDLC Governance Model
- Security vulnerabilities
- Compliance failures
- Vendor risks
- Data privacy exposures
- AI algorithm bias risks
- Operational resilience gaps
The NIST Risk Management Framework and ISO 31000 provide structured approaches to identifying and mitigating these risks.
Practical Risk Mitigation Strategies
Effective risk management in software development includes:
- Maintaining a dynamic risk register
- Assigning risk ownership
- Automating compliance checks
- Conducting architecture risk reviews
- Performing third-party assessments
Organizations that formalize risk management in software development consistently report fewer high-severity incidents and faster audit readiness, according to enterprise governance research.
SDLC Audit Checklist for Enterprise Readiness
An SDLC audit checklist ensures consistent governance across projects. It also provides documentation evidence during regulatory audits.
Planning Phase Audit
01
- Approved business case
- Documented risk assessment
- Budget authorization
- Regulatory impact analysis
Design Phase Audit
02
- Architecture review approval
- Security design validation
- Data classification mapping
Development Phase Audit
03
- Code review documentation
- Secure coding adherence
- Dependency scan results
Testing Phase Audit
04
- Test traceability matrix
- Security testing reports
- Performance benchmarks
Deployment Phase Audit
05
- Change approval record
- Rollback plan
- Monitoring configuration evidence
Metrics That Measure Software Lifecycle Governance
An SDLC governance model must be measurable to be effective.
Key Governance KPIs
- Schedule variance (%)
- Budget variance (%)
- Risk exposure index
- Defect leakage rate
- Audit findings per release
- Control compliance rate
Organizations with defined governance KPIs achieve greater predictability and stronger board-level confidence.
Governance Maturity Levels
Initial
Managed
Defined
Quantitatively Managed
Optimizing
Enterprises operating at Level 4 or above demonstrate structured software lifecycle governance aligned with enterprise risk strategies.
Implementation Roadmap for an SDLC Governance Model
Implementing an SDLC governance model requires executive commitment and phased rollout.
Secure Executive Sponsorship
Tie governance objectives to risk reduction and financial protection.
Define Governance Charter
Clarify: Decision rights, Escalation procedures, Accountability roles.
Standardize the Phase Gate Process
Define entry and exit criteria for each stage. Document required deliverables.
Embed Risk Management in Software Development
Integrate risk scoring dashboards and automated policy checks.
Pilot and Scale
Start with high-risk programs. Refine before enterprise-wide adoption.
Continuous Improvement
Use metrics to refine governance effectiveness and eliminate bottlenecks.
Common Pitfalls in Implementing an SDLC Governance Model
Avoid these mistakes:
- Overly bureaucratic approvals
- Governance treated as documentation only
- No automation
- Lack of executive accountability
- Ignoring vendor ecosystem risk
An effective SDLC governance model balances control with agility.
Real-World Case Study
Real-World Case Study
A global healthcare enterprise adopted:
- Structured SDLC governance model
- Automated phase gate process
- Enterprise-wide SDLC audit checklist
- Formal risk management in software development
Results within 12 months:
- 28% reduction in compliance findings
- 19% improved delivery predictability
- 33% faster audit readiness
- Governance maturity increased from Level 2 to Level 4
Why an SDLC Governance Model Is a Competitive Advantage
Enterprises with a mature SDLC governance model benefit from:
- Reduced regulatory penalties
- Improved investor confidence
- Stronger cybersecurity posture
- Faster audit cycles
- Enhanced cross-functional alignment
Software lifecycle governance is no longer optional in AI-driven digital ecosystems.
How Betatest Solutions Supports Enterprise SDLC Governance
Building and enforcing a governance model across a large software portfolio takes more than policy documents — it takes the right technical partner at every gate. Betatest Solutions supports enterprise teams by:
- Structuring phase gate processes aligned to ISO/IEC 12207 and COBIT principles
- Embedding risk management and compliance checks directly into development and deployment pipelines
- Delivering the underlying software development work — from planning through the 7 phases of the SDLC — with governance built in from day one
- Supporting enterprise web development initiatives that need to meet audit and compliance standards from the start
If your organization is scaling governance across multiple software initiatives, a structured, enterprise-ready development partner makes the difference between governance on paper and governance in practice.
Conclusion: Governance Is Strategic, Not Administrative
A well-designed SDLC governance model transforms software delivery from reactive to predictable.
By integrating a formal phase gate process, structured SDLC audit checklist, and disciplined risk management in software development, enterprises gain transparency and resilience.
In a regulatory-first digital economy, governance maturity directly impacts brand trust and market competitiveness.
Frequently Asked Questions
What is SDLC governance?
SDLC governance is a structured framework of policies, approval gates, and accountability mechanisms that controls how software initiatives move from concept to retirement, ensuring compliance, risk management, and predictable delivery.
What is a phase gate in software development?
A phase gate is a formal review checkpoint between development stages where deliverables, risk, budget, and compliance are evaluated before the project is allowed to proceed to the next stage.
What is a software governance model?
A software governance model — also called an SDLC governance model or software development governance model — defines the oversight structures, decision rights, and controls that guide how software is planned, built, and maintained across an organization.
Can governance and Agile coexist?
Yes. Modern enterprises embed governance directly into Agile and DevOps workflows using automated digital gates and CI/CD-integrated approvals, rather than applying governance as a separate, slower process.
Ready to implement SDLC in your project?
Get expert guidance on the SDLC model that fits your project — no one-size-fits-all approach.